Blackwall has raised $100 million at a $2.2 billion valuation, putting fresh capital behind a business that helps hosting providers control the traffic reaching their customers’ websites.
The company’s Series C announcement names AVP as lead investor, alongside existing backers Dawn Capital, MMC Ventures and Tera Ventures. TechCrunch also reported the financing on October 20.
Blackwall says the money will support expansion across 12 strategic regions in North America, Europe, Asia-Pacific and the Middle East, as well as further product development.
For businesses building AI agents, the significance extends beyond another security funding round. An assistant may be capable of researching a product or navigating a website, but completing that task still depends on whether the website’s infrastructure lets it through.
Hosting providers are central to the business
Blackwall’s current pitch is built around service providers. Its platform can be integrated into a provider’s environment, offered under that provider’s branding and packaged into different security tiers. The host retains the customer relationship and decides how to sell the protection.
That makes distribution part of the product strategy. A hosting company already serving a business’s website can also offer traffic protection through its existing service, without asking the customer to assemble a separate security stack.
Blackwall lists bot mitigation, application-layer DDoS protection, a web application firewall, traffic analytics and custom rules among its capabilities. It presents these tools as a way for providers to develop recurring security revenue.
The commercial proposition has two sides: reduce unwanted activity reaching hosted applications and sell protection to customers. Whether those benefits justify the cost will depend on each provider’s traffic, configuration and customer demand.
What the infrastructure actually does
Blackwall’s technical documentation describes GateKeeper as a reverse proxy that hosting providers can run inside their own infrastructure. A reverse proxy receives requests before the application behind it, creating a point where traffic can be inspected or restricted.
The documented architecture combines request filtering, rate limits and behavioural analysis. Its management dashboard handles functions such as traffic controls, configuration and subaccounts. The documentation also describes a managed option for individual websites.
These are descriptions of how the system is designed to operate, rather than an independent measurement of its ability to identify every legitimate agent. An important distinction remains: recognising automation and deciding whether that automation should be allowed are different decisions.
A useful agent can still encounter an access rule
Consider a customer asking an assistant to compare three products. The assistant might need to open several pages, check specifications and revisit prices. From the customer’s perspective, that is an ordinary shopping task. From the website’s perspective, it is a sequence of automated requests.
The difficulty is deciding where acceptable research ends and unwanted collection begins. Blocking too aggressively could prevent a useful visit; allowing too broadly could expose a site to activity its owner never intended to permit.
Blackwall’s published rule categories illustrate this policy problem. Administrators can set access behaviour for groups including search engines, cloud services, content scrapers and bots that emulate humans. Some categories support CAPTCHA challenges as well as access decisions.
Those controls give site operators choices. They do not, by themselves, establish that an agent has permission to perform a particular customer action. A request to read a public product page and a request to change account details require different treatment.
This is the website-facing counterpart to the permissions problem explored in our coverage of Microsoft’s Guardian Agents: an agent’s ability to act needs boundaries both within the organisation running it and at the services it contacts.
What buyers should ask next
For a hosting provider evaluating Blackwall, the useful evidence would include how often legitimate visits are blocked, how much abusive traffic still reaches applications and what extra delay the controls introduce.
Agent developers have a related concern: can a failed task be traced to an access decision? A clear denial or challenge is more useful than an assistant repeatedly retrying a page without explaining why it cannot proceed.
A practical evaluation should therefore include ordinary browsing, permitted automation and controlled abusive traffic, with outcomes recorded separately. It should also check whether an administrator can understand and correct a mistaken decision. This is an evaluation approach, not a claim that Blackwall has passed such a test.
Blackwall’s funding gives it resources to expand its place in hosting infrastructure. The harder operational question is how precisely that infrastructure can enforce a website’s rules while preserving the automated visits its owner actually wants.
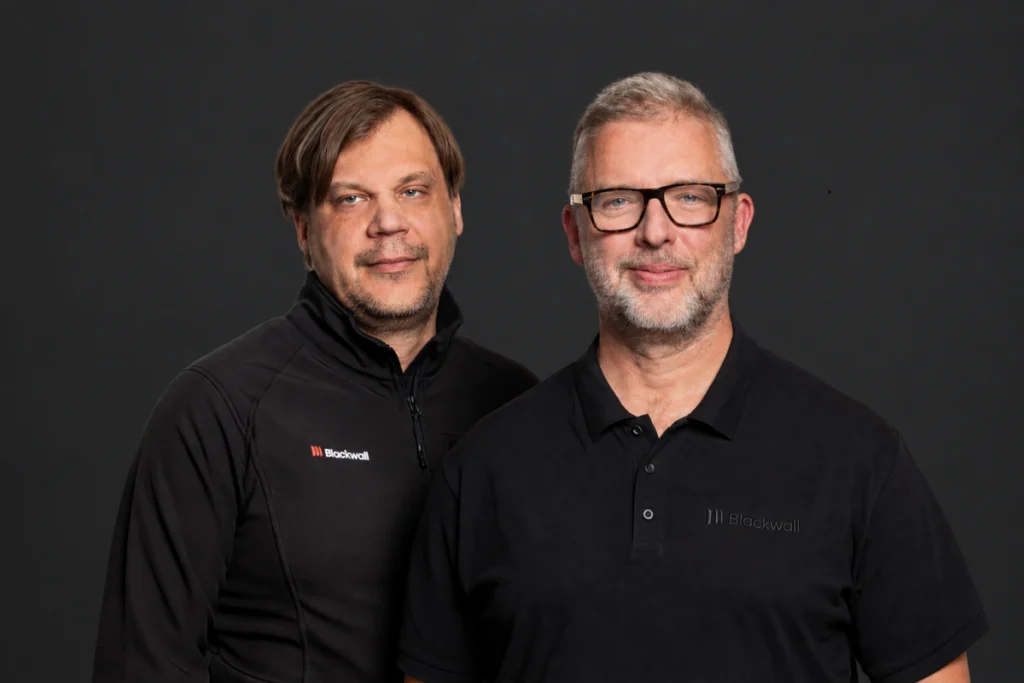
Featured image: Blackwall co-founders Denis Prochko (left) and Nik Rozenberg. Image credit: Blackwall.
About Puneet Sharma
Puneet Sharma · Freelance Writer
Puneet Sharma is a freelance writer covering AI agents, automation and the software changing how we work. His coverage at AgentsCalling starts with the questions a reader might ask over a conversation: What does this tool actually do? Where does it fall short? And is it useful beyond the demo? His articles explore new launches, practical workflows and the trade-offs behind giving software more responsibility, with explanations that make room for readers who are still getting familiar with AI.